

ISO 27001 advice, implementation and internal audit
ISO 27001 certification with a pass rate of 100%
Every organization that we guide through ISO 27001 passes the external audit. We practically implement your ISMS, conduct the internal audit, and prepare your team for certification.
- After the first conversation, a clear price quote
- Internal audit by certified lead auditors, standard in the process
- Ready in an average of 4 to 5 months, with 3 to 6 hours per week from your team

Trusted by 500+ companies·ISO/IEC 27001:2022·Also NEN 7510, BIO and NIS2

“The lines of communication with Nestor Security were short. The organization is pragmatic and a sober party to do business with.â€
Pascal Kamphuis·Corpoflow
Schedule a no-obligation consultation
One of our ISO 27001 experts will contact you. In that conversation, we will discuss your situation, the lead time, and the costs.
How can we help you? (optional)
Find out why 500+ Companies trust Nestor Security for IT security and compliance


In this way, Nestor Security compares itself to other options
If you are considering multiple quotes, how does an ISO 27001 project with Nestor Security compare to other consulting firms and compliance platforms?.
| Nestor Security | Other advisory firms | Compliance platforms | |
|---|---|---|---|
| Approach | Policies and procedures that suit your organization, so that your employees can actually use them | Often based on standard templates | Templates and checklists, the filling in is up to you |
| Lead time | On average 4 to 5 months until certification | Often 6 months or longer | Depending on your own pace |
| Commitment to own team | On average 3 to 6 hours per week | Varies greatly by agency | Most of the work lies with your team |
| Risk analysis | Comprehensive risk analysis workshop with your team | Usually included; the depth of coverage varies by agency | Risk register in the software, without guidance |
| Implementation | From policy to technical measures, together with your team | Often advice is given on paper; the implementation is up to you. | Automatic checks and evidence collection |
| Internal audit | Through certified lead auditors, well before the external audit | Sometimes purchased separately from a third-party source | Not included, often through a partner |
| External audit | Full support and presentation of the audit certificate | Support varies by agency | Exporting evidence to the auditor |
| Result | 100% of our customers pass the external audit | Success rate rarely known | Depending on your own commitment |
| After certification | Assistance with surveillance audits, management reviews, and recertification | Often a new path per audit | Continuous monitoring; the follow-up is up to you |
| Costs | Clear pricing upfront, after a free consultation | Often on an hourly basis, with the possibility of overtime | Monthly license, guidance and audits separately |
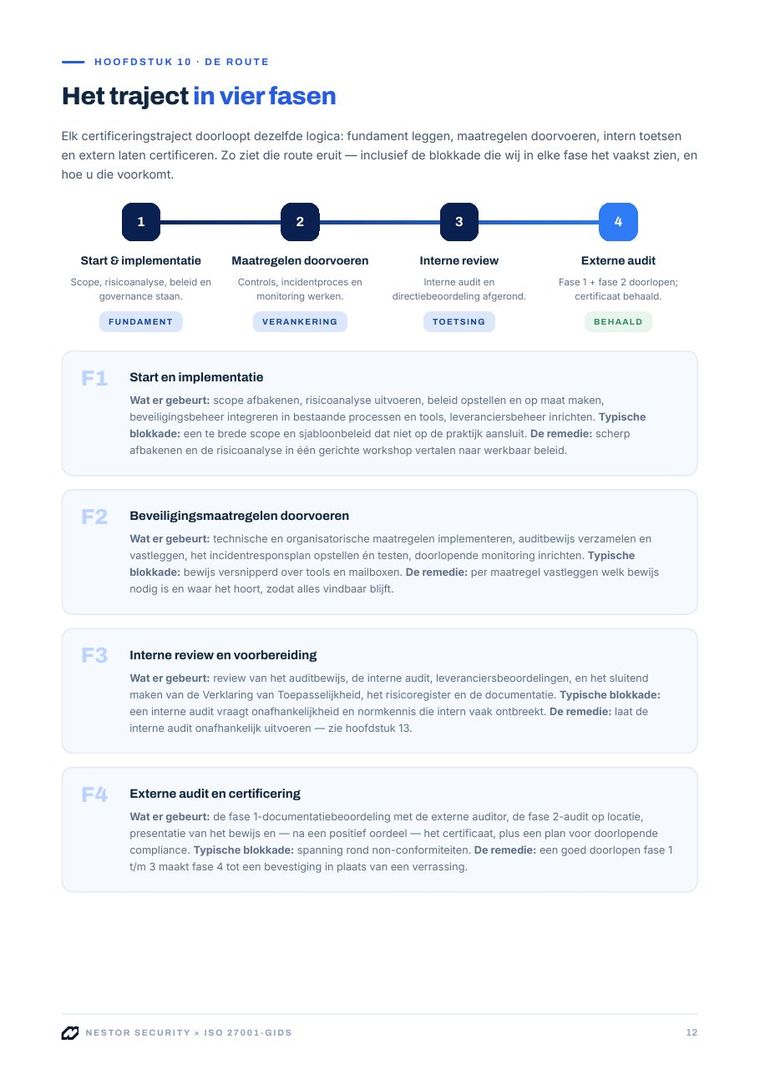
Our approach to ISO 27001 implementation
A structured, expert-led approach that takes the uncertainty out of the process.
Start and implementation
- Integrate security management into existing processes and tools
- Rollout and customization of policy
- Comprehensive risk analysis workshop
- Setting up a vendor management framework
Implement security measures
- Implementation of technical security measures
- Collection and recording of audit evidence
- Drafting and testing the incident response plan
- Setting up continuous monitoring
Internal review and preparation
- Comprehensive review of the audit evidence
- Performing the internal audit
- Vendor security assessments
- Finalizing the Statement of Applicability
- Completing the risk register and documentation
External audit and certification
- Phase 1 - Document review with the external auditor
- Conduct Phase 2 audit
- Full audit support and evidence presentation
- Achieving certification and an ongoing compliance plan
Certificate obtained
Your ISO 27001 certificate is valid for three years, with surveillance audits in years 1 and 2 and recertification in year 3. We will also remain on board after that.
On average, you are ready for certification in 4 to 5 months, with a commitment of 3 to 6 hours per week from your team. The exact schedule depends on the size of your organization and the measures that have already been implemented.
Only an internal audit needed?
Our certified lead auditors assess your ISMS and management measures, identify any bottlenecks, and tell you exactly what needs to be done next. This way, you pass the external audit without any surprises. The certificate itself always comes from an independent certification body.
ISO 27001 Implementation Guide
✓Costs and lead time: realistic bandwidths per organization size
✓Understanding what certification requires from your organization
✓Overview of the steps toward the external audit
✓Free and without obligations
Success story: Effectory
Feedback analytics developers with a team of over 250 people
Months before a project with ISO 27001 and ISO 27701
New security measures implemented
Success during the external audit

The challenge
Effectory processes sensitive employee data for over 1,200 organizations. The challenge was to continuously strengthen the information security system and have it grow with the high demands of customers, without disrupting daily services.

The approach
In close collaboration, we have refined the management system for both ISO 27001 and ISO 27701. With a dedicated point of contact, responsibilities have been clearly defined, processes secured, and the organization prepared for the external audit to achieve certification.

The outcome
Within 6 months, Effectory achieved ISO 27001 certification without any bottlenecks. Security is now demonstrably in order for customers, security questionnaires are answered more quickly, and a solid, future-proof foundation is in place.

Nestor Security conducted the internal audits for both ISO 27001 and ISO 27701 for us. They really strike the right chord for us with a great combination of quality and feasibility. They are pragmatic, think along well with our needs, and the audits are well-organized.
 Wouter Buzing
CISO, Effectory
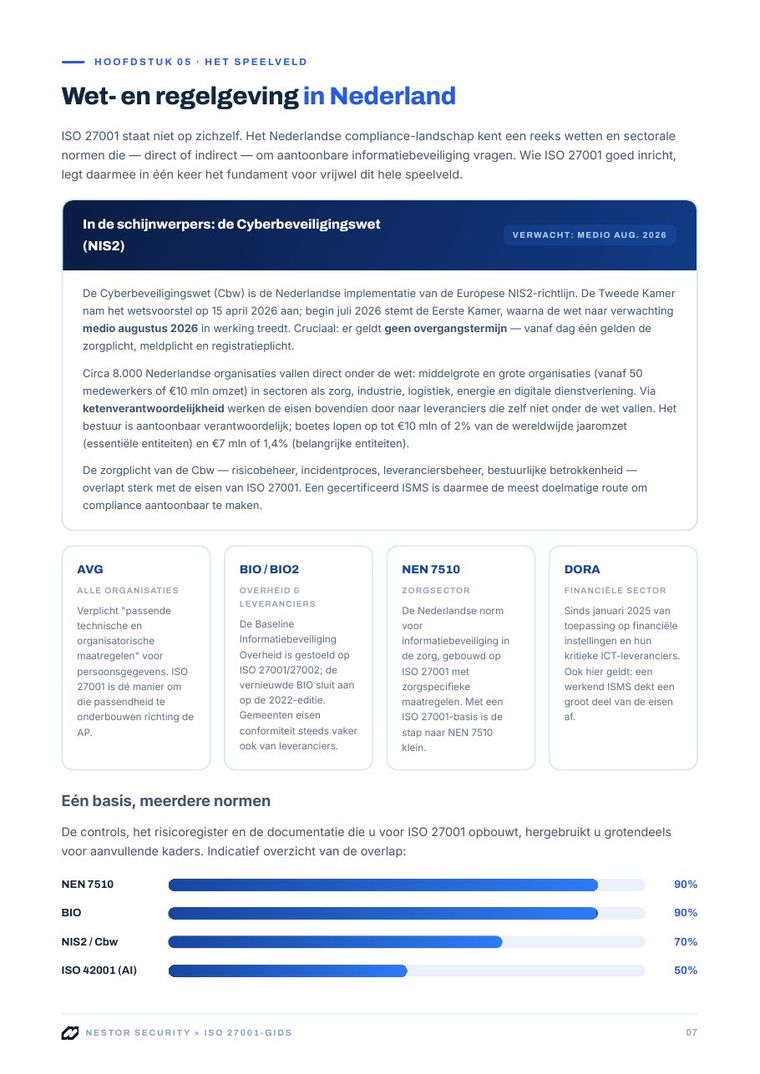
The foundation you lay with ISO 27001 strengthens future compliance
ISO 27001 certification provides a significant head start on implementing additional standards, thanks to shared controls and processes.
More than 90% overlap with NEN 7510
More than 90% overlap with BIO
More than 70% overlap with NIS2
A 50% overlap with ISO 42001
Don't just take it from us
You are in good company with Nestor.
“Communication with Nestor Security was direct. The organization has a pragmatic approach and is a down-to-earth partner to do business with. As a result, the process went smoothly and quite quickly.â€
“We prefer to collaborate regionally as much as possible and like to hold meetings face-to-face. When you look at partners in the North, a few remain – and Nestor Security stood head and shoulders above the rest.â€

"Nestor Security has provided us with the internal audits of ISO 27001 and ISO 27701. They really hit the right chord for us with a good combination of quality and practicability. They think pragmatically, well with our needs and the audits were well taken care of."

Your questions answered
FAQs
What does an ISO 27001 journey cost?
The costs depend on the size of your organization, the scope of the ISMS and the measures that are already in place. After a free consultation, you will receive a clear, customized price quote.
Realistic bandwidths per organizational size and all cost items are listed in the ISO 27001 Implementation Guide.
How long does an internal audit take?
That depends on the size of your organization, the scope of the ISMS, and the number of locations. For an SME organization, the audit itself is often completed in one to several days, followed by the reporting. During the scoping phase, we will provide you with a concrete schedule in advance, so you know how much time you need to free up for your employees.
How long does the ISO 27001 certification process take?
On average 4 to 5 months. The exact duration depends on the size of your organization and what has already been arranged, and the external audit’s planning also depends on the certifying institution.
In the initial conversation, we discuss what planning is realistic for your organization.
What does the process of our own team require?
On average 3 to 6 hours per week, divided between the colleagues involved. We work not only for you, but also with you. Your team provides the knowledge of your own processes and systems, and is involved in, among other things, the risk analysis workshop.
In the internal audit, we speak with the owner of the ISMS, someone from the management, and the process owners of the components we audit, such as HR, IT, facilities, and purchasing. We agree in advance on who we need when necessary, so that the interviews remain short and focused.
What is the difference between an internal and an external ISO audit?
You organize the internal audit yourself, or have it performed by an independent party such as Nestor Security. The goal is to discover where the ISMS does not yet comply and to improve that before anyone else sees it. The external audit is conducted by a certification body and determines whether you obtain or retain the certificate.
As an external party, we are allowed to conduct your internal audit, but not your certification audit. Those two roles always remain separate, and that is precisely what makes the internal audit so valuable: you get the perspective of an auditor, with nothing at stake.
Ready to make compliance simple?
Schedule a free consultation with one of our ISO 27001 experts.
Schedule a no-obligation consultationRequest Implementation Guide
100% Pass Rate·500+ customers·Also NEN 7510, BIO and NIS2