ISO 27001 internal audit
Achieve and maintain ISO 27001 compliance with a comprehensive internal audit conducted by our experienced auditors, who boast a 100% success rate.
Achieve and maintain ISO 27001 compliance with a comprehensive internal audit conducted by our experienced auditors, who boast a 100% success rate.

Our experienced ISO 27001 auditors will assess your ISMS and control measures, identify bottlenecks, and tell you exactly what still needs to be done so that you pass the external audit without surprises.
Accredited lead auditors·On-site / remote·100% Success Rate Among Our Customers


Colleagues review each other's work
Independent, planned and demonstrable
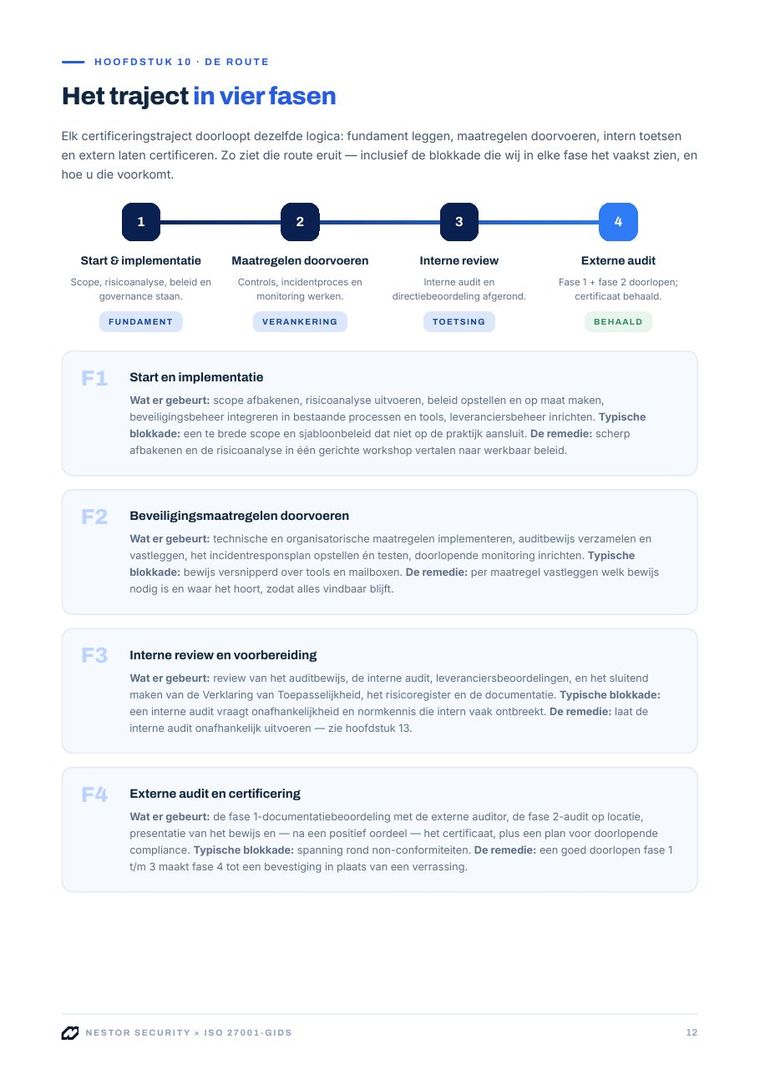
From scoping to next steps: a clear process in which you know at all times what is happening, who we need, and what it yields.
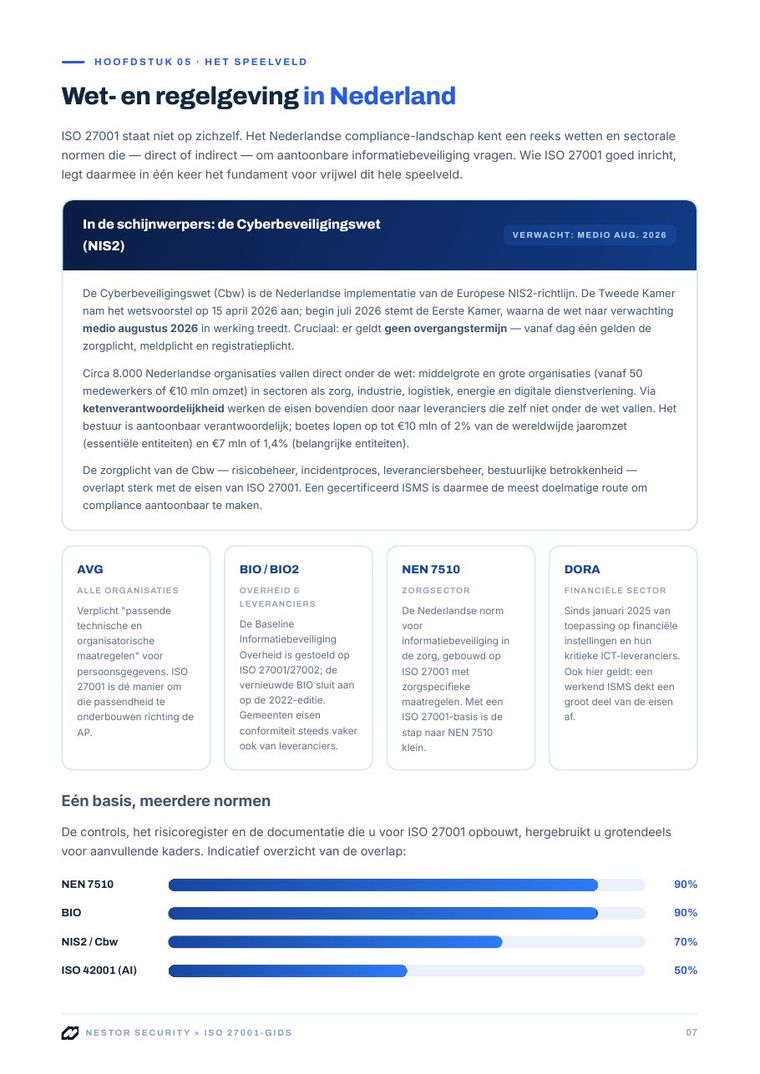
Following the internal audit, you know exactly where you stand. The findings have been resolved or scheduled, the evidence is ready, and your team knows what the external auditor will ask.
✓Understanding what your organization's internal and external audits require
✓Overview of the steps toward certification and how to maintain it
✓Free to download, no obligations
Feedback analytics developers with a team of over 250 people

Effectory processes sensitive employee data for over 1,200 organizations and is certified for both ISO 27001 and ISO 27701. The annual internal audits needed to be independent and thorough, without disrupting daily operations.

Nestor Security handles the internal audits for both standards. With a dedicated contact person, a clear audit plan, and interviews with the right people, we test the management system precisely on the points that the external auditor focuses on.

Effectory passes the external audits without any bottlenecks. The findings from the internal audits are concrete and actionable, making the ISMS stronger every year and enabling faster completion of customer security questionnaires.

Nestor Security conducted the internal audits for both ISO 27001 and ISO 27701 for us. They really strike the right chord for us with a great combination of quality and feasibility. They are pragmatic, think along well with our needs, and the audits are well-organized.
 Wouter Buzing
Do you also work with NEN 7510, BIO, NIS2, or ISO 42001? Thanks to the significant overlap in control measures and processes, our auditors combine the internal audit wherever possible. That saves time for your employees and prevents duplicate interviews.
More than 90% overlap with NEN 7510
More than 90% overlap with BIO
More than 70% overlap with NIS2
A 50% overlap with ISO 42001
An internal audit is not a check-the-box exercise. We look for what can genuinely be improved and translate that into steps your organization can implement immediately.
We test rigorously, exactly as the certifying body does. At the same time, we keep the recommendations workable, so your team can get to work on them the next day instead of dreading them.
From policy and risk assessment to the 93 controls: we assess the entire management system through interviews and documentation, and ask for the evidence that the external auditor will want to see later.
Our auditors will come to you or work remotely. You choose what fits your organization and schedule, with minimal disruption to your daily work.
We explain why a finding is a finding. This helps your employees better understand the standard and puts your organization in a much stronger position for the next audit, internal or external.
You are in good company with Nestor.
“Communication with Nestor Security was direct. The organization has a pragmatic approach and is a down-to-earth partner to do business with. As a result, the process went smoothly and quite quickly.â€
“We prefer to collaborate regionally as much as possible and like to hold meetings face-to-face. When you look at partners in the North, a few remain, and Nestor Security stood head and shoulders above the rest.â€
“Nestor Security conducted the internal audits for ISO 27001 and ISO 27701 for us. They truly hit the right chord for us with a great combination of quality and feasibility. They are pragmatic, think along with our needs, and the audits are well executed.â€
You are facing your first external audit and want to be sure your ISMS is correct. Our internal audit shows what still needs to be done, so you can invite the certifying body with confidence.
Your certificate is valid for three years, with annual surveillance audits. We conduct the mandatory internal audit and keep your ISMS sharp between external milestones, ensuring it does not become a paper tiger.
After three years, your entire management system is reassessed. A thorough internal audit beforehand prevents old non-conformities from suddenly reappearing and ensures you start the new cycle with a clean slate.
An ISO 27001 audit is a systematic assessment of your Information Security Management System (ISMS). The auditor evaluates whether your policies, processes, and controls meet the standard's requirements and whether they actually work in practice. This is done through interviews with employees, reviewing documentation, and requesting evidence.
There are two types: the internal audit, which you organize yourself or have performed by an independent party such as Nestor Security, and the external audit by a certifying body. The internal audit is mandatory and forms the best preparation for the external one.
That depends on the size of your organization, the scope of the ISMS, and the number of locations. For an SME organization, the audit itself is often completed in one to several days, followed by the reporting. During the scoping phase, we will provide you with a concrete schedule in advance, so you know how much time you need to free up for your employees.
The internal audit covers the entire ISMS: the context of the organization, leadership and policy, risk assessment and risk treatment, support, operation, evaluation, and improvement. In addition, we test the security controls from Annex A that are included in your Statement of Applicability.
You can choose to have everything audited at once, or spread it over multiple audits during the year. Both methods are permitted, as long as the entire system is covered within the cycle.
In any case, the owner of the ISMS, usually the CISO or security officer, and someone from the executive board. Furthermore, we speak with the process owners of the departments we assess, such as HR, IT, facilities, and procurement. During the closing meeting, we share the findings with management.
We coordinate in advance who we need and when, so that interviews remain brief and focused and no one has to take a whole day off.
You organize the internal audit yourself, or have it performed by an independent party such as Nestor Security. The goal is to discover where the ISMS does not yet comply and to improve that before anyone else sees it. The external audit is conducted by a certification body and determines whether you obtain or retain the certificate.
As an external party, we are allowed to conduct your internal audit, but not your certification audit. Those two roles always remain separate, and that is precisely what makes the internal audit so valuable: you get the perspective of an auditor, with nothing at stake.