

ISO 27001 advice
ISO 27001 advice from consultants who be a lead auditor yourself
We will tell you honestly where you stand, what still needs to be done and what the cost will be. Then you decide for yourself how much guidance you want, from mentoring and reviews to the entire certification process.
- Start with a baseline measurement and know where you stand within three weeks
- One fixed point of contact, no changing consultants
- Tailor-made policies instead of standard templates

Trusted by 500+ companies100% Pass RateAlso NEN 7510, BIO and NIS2

When you look at partners in the North, there are still a number of them left, and Nestor Security stood out above the rest.
Irene BernsenJoyce-House
Schedule a free consultation
In half an hour we will discuss your situation and perform a short quick scan. You will immediately hear what a realistic course of action is.
How can we help you?
Response from an ISO 27001 consultant within one working day. Free of charge and without sales talk.
Find out why 500+ Companies trust Nestor Security for IT security and compliance


In this way, our advice relates to other options.
If you are obtaining several quotes, these are the differences that matter in practice.
| Nestor Security | Other advisory firms | Compliance platforms | |
|---|---|---|---|
| Starting point | Zero measurement with a concrete roadmap and budget | Often a quote for the entire journey immediately | Self-scan in the software |
| Advice | Practical and tailored to your organization | Often based on standard templates | Generic templates, the filling in is up to you |
| Contact person | A dedicated consultant from start to finish | Often changing consultants | Support desk or chat |
| Audit experience | Consultants who are themselves lead auditors | Varies per agency | Auditors through partners |
| Flexibility | From advice on request to the entire process | Often only the entire process | Fixed license, guidance separately |
| Internal audit | By a certified lead auditor | Sometimes purchased separately | Not included |
| Costs | Fixed price per phase, known in advance | Often on an hourly basis | Annual license plus advice and audits |
| Result | 100% of our customers have passed the external audit | Success rate rarely known | Depending on your own commitment |
Within three weeks you will know exactly where you stand
With a zero-measurement assessment, we test your organization against all the requirements of ISO 27001 and the 93 measures from Annex A. You will get a clear picture of what is already compliant, what is missing, and how much work that is.
- Testing against clauses 4 to 10 and Annex A
- Interviews with management, IT and process owners
- Report with priorities, planning and budget
- Fixed price, known in advance
9 parts tested
Choose how much support you want
After the zero measurement, you decide on the shape. You can always choose more or less guidance later on.
Advice on request
You do the work yourself; we discuss, review, and answer your questions.
Guided implementation
We implement the ISMS together with your team, from a zero-based assessment to the certificate.
ISMS management
After the certification, we keep your ISMS up to date and ready for any audit.
This is how our ISO 27001 advice works
From the first conversation to the certificate, in the format that suits you. You know what each step will deliver and what it will cost at every step.
Consultation and quick scan
- Your reason, such as a customer request, tender, NIS2 or your own ambition
- Brief quick scan of what is already available
- Honest advice: Is ISO 27001 the right step?
Zero measurement
- Review of all requirements and the 93 measures from Annex A
- Interviews with key figures
- Report with what already works and what is missing
Action plan and budget
- A scope that is logical for customers and auditors
- Priorities based on where your risk is greatest
- Realistic planning and a fixed price per phase
Guidance in the form of your choice
- Advisory on request, guided implementation or ISMS management
- Internal audit by a lead auditor who was not involved in the implementation
- Support during the external audit
Control over information security
With an ISMS that suits your organization and a certificate that convinces customers. On average, you are ready for the external audit in 4 to 5 months.
Success story of Effectory
Feedback analytics developers with a team of more than 250 people
Months before a project with ISO 27001 and ISO 27701
New security measures implemented
Success during the external audit

The challenge
Effectory processes sensitive employee data for over 1,200 organizations. The challenge was to continuously strengthen the information security system and have it grow with the high demands of customers, without disrupting daily services.

The approach
In close collaboration, we have refined the management system for both ISO 27001 and ISO 27701. With a dedicated point of contact, responsibilities have been clearly defined, processes secured, and the organization prepared for the external audit to achieve certification.

The outcome
Within 6 months, Effectory achieved ISO 27001 certification without any bottlenecks. Security is now demonstrably in order for customers, security questionnaires are answered more quickly, and a solid, future-proof foundation is in place.

Nestor Security conducted the internal audits for both ISO 27001 and ISO 27701 for us. They really strike the right chord for us with a great combination of quality and feasibility. They are pragmatic, think along well with our needs, and the audits are well-organized.
 Wouter Buzing
CISO, Effectory
Finding out on your own costs more than it seems
The standard sets out what you need to arrange, not how. It is often this translation that goes wrong, with too many documents, too little evidence, or measures that do not fit the risk situation.
Without advice
Searching, hesitating, and overdoing it
Met Nestor Security
Clear, practical and sure
Only an internal audit needed?
Our certified lead auditors assess your ISMS in the same way the certifying body will do in the future, and tell you exactly what still needs to be done. Always at a fixed price.
ISO 27001 Implementation Guide
- Realistic Costs and Lead Times by Organization Size
- Understanding what certification requires from your organization
- Overview of the steps toward the external audit
- Free and without obligations
Don't just take it from us
You are in good company with Nestor.
The communication lines with Nestor Security were short. The organization has a pragmatic mindset and is a down-to-earth party to do business with. As a result, the process went smoothly and fairly quickly.

We prefer to work together as much as possible regionally and like to hold meetings face-to-face. When you look at partners in the North, there are still a few left, and Nestor Security stands out above the rest.
Nestor Security has provided the internal audits of ISO 27001 and ISO 27701 for us. They really hit the mark for us with a good combination of quality and practicality. They are pragmatic, think well with our needs, and the audits are well-managed.

Your questions answered
FAQs
Where do I start with ISO 27001?
With the question of why you want it and for which part of the organization. After that comes a zero-based assessment, which shows what is already in place and what is still missing.
Many organizations underestimate how much is already being handled, and overestimate how much documentation the standard really requires.
Should we outsource everything?
No. Some clients do most of the work themselves and use us as a sparring partner and reviewer. Others let us handle the entire process.
Whatever you choose, the knowledge remains within your organization, so you can maintain the ISMS yourself later on.
What exactly does ISO 27001 advice entail?
We help you translate the requirements of ISO 27001 into your organization. That starts with a zero-based assessment and an action plan, and can continue through to full implementation, internal audit, and guidance for external audits.
You decide for yourself how much you outsource.
What determines the price of ISO 27001 advice?
Especially the size of your organization, the scope and how much guidance you want. After the consultation, you will receive a fixed price quote per phase, so you know in advance what you are getting involved in.
You can find guidelines based on organizational size in the ISO 27001 Implementation Guide.
Do you also help with NIS2, NEN 7510 or the BIO?
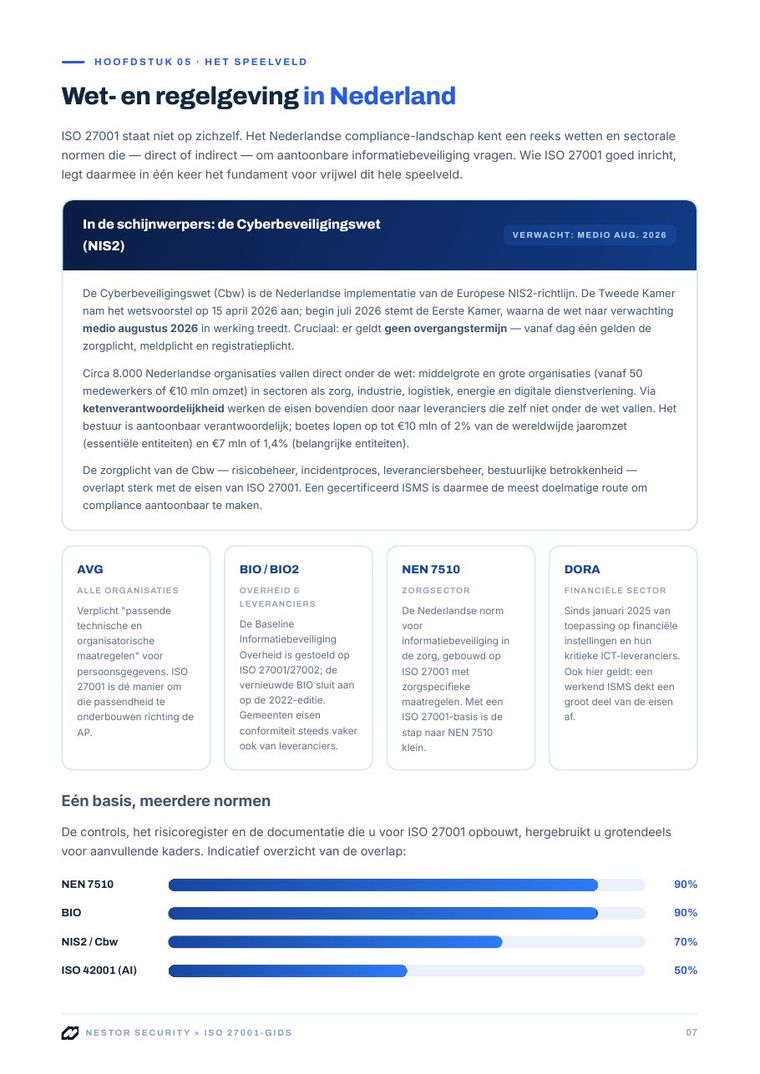
Yes. Since August 15, 2026, the Cyber Security Act has been in effect, the Dutch version of NIS2. ISO 27001 overlaps with more than 70% of these requirements, and with more than 90% with NEN 7510 and the BIO.
We configure your ISMS so that you cover multiple standards at the same time.
How long will it take before we are certified?
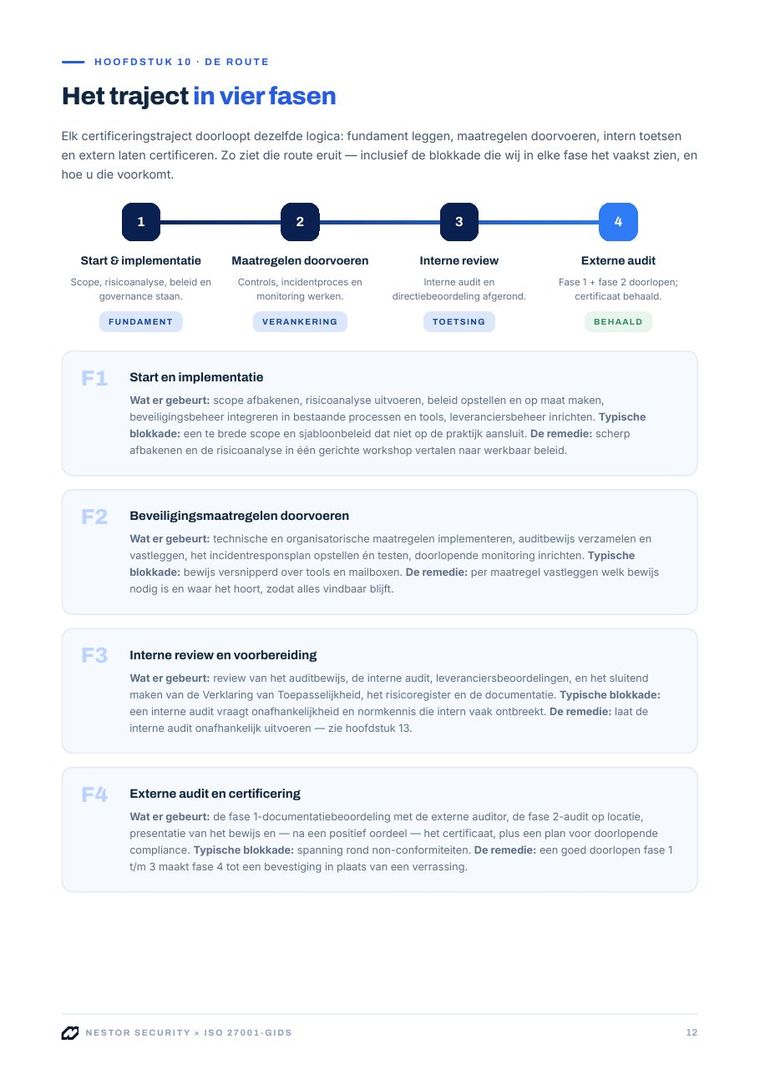
On average, 4 to 5 months from the start of implementation. If you already have a good foundation, it can be faster. After the initial assessment, you will receive a plan that suits your situation.
Are you independent of certification bodies?
Yes. We advise and conduct internal audits; the certification is always carried out by an independent institution that is accredited by the Accreditation Council.
We can help you compare quotes and choose an institution that suits your sector.
Start with honest advice
Schedule a free consultation. You’ll immediately hear where you stand, what a realistic course of action is, and what the costs will be.
Schedule an appointment for adviceRequest Implementation Guide
Start with a zero measurementOne fixed point of contact100% Pass Rate