For many organizations, digital resilience has long ceased to be a casual choice, but a necessity. European legislation is raising the bar for cybersecurity and risk management with NIS2.
At an earlier article We noted that the Dutch government has been urging organizations to prepare for the upcoming ‘Cybersecurity Act’, as the NIS2 directive is implemented in the Netherlands. But what does that mean for organizations in the Netherlands? And what can you do to prepare your organization?
Who is covered by the Cyber Security Act?
The Cybersecurity Act (NIS2 Directive Implementation Act) does not apply to every organization. Organizations in highly critical sectors, such as energy, health care and transportation, are covered by this law. Organizations in critical areas, such as waste management, postal services and digital services, must comply with the law.
The central government offers a NIS2 Self-evaluation EN to which you can find out if your organization is covered by NIS2.
The next steps
The government provides tools to check how you stand in accordance with the thrust of the European NIS2 Directive through a NIS2 Quickscan. The Quickscan gives you advice and tools to take the first steps in the right direction with technical or organizational measures. The scan is intended as an initial tool and does not guarantee that your organization already complies with the future cyber security law in the Netherlands.
Achieving a ISO 27001 certificate is not a legal requirement under the Cybersecurity Act, but it can be a valuable first step. As part of ISO 27001 implementation, your organization sets up an Information Security Management System (ISMS): a structured framework that identifies risks, establishes security measures and makes it easier to demonstrate compliance. An ISMS is not an explicit requirement under the Cybersecurity Act. The law does require that organizations take appropriate technical and organizational measures to manage risks to network and information systems. In practice, this means that many organizations have a structured and demonstrable approach to information security, often designed according to the principles of an ISMS. With ISO 27001 certification, your organization will comply with the Cybersecurity Act even before 90%. With several additional measures, you will ensure that your organization is fully NIS2 compliant.
An additional measure from the Cybersecurity Act is that the boards of organizations are administratively and jointly and severally liable for complying with the law. In an earlier article we elaborate on what this means. In addition, they must attend annual risk management training. Such trainings These are already being offered and it is advisable not to wait until the new law requires you to follow them. Following a training session provides board members with an insight into what is expected of them once the Cyber Security Act comes into effect.
Commitments in brief
Organizations subject to the Cybersecurity Act will face, among other things, duty of care, duty of notification and duty of registration:
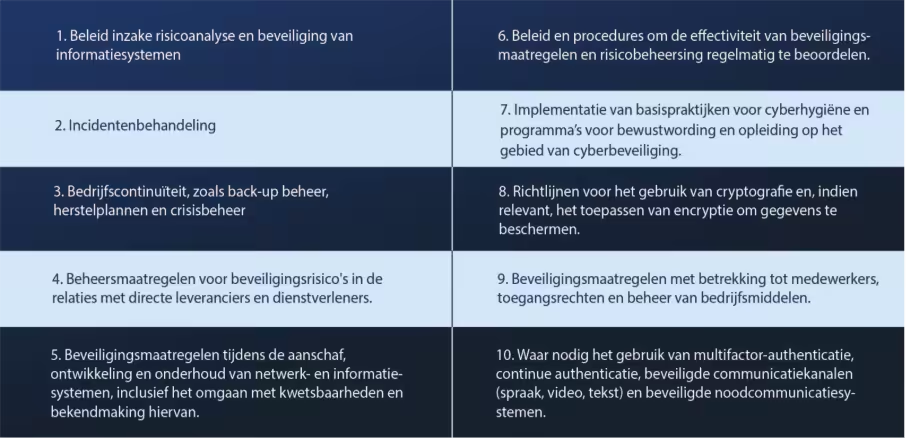
- Duty of care: An organization must demonstrate that it has taken measures to prevent cyberattacks and limit their impact. The Cyber Security Act includes the following 10 duty of care measures:
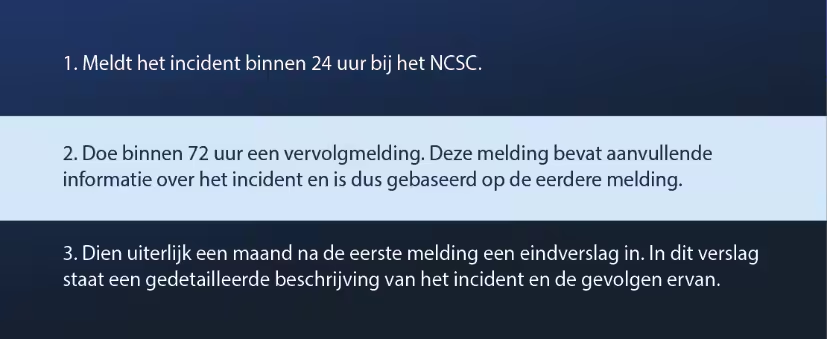
- Mandatory reporting: An organization is required to report significant incidents to the appropriate authority. NCSC provides the ability to report incidents and serves as a Computer Security Incident Response Team (CSIRT). The following steps should be followed when reporting an incident:
- Registration requirement: Any organization covered by the NIS2 Directive must be registered with the appropriate authority, the NCSC. You don't have to wait for the Cybersecurity Act to take effect. You can register your company by logging on to my.ncsc.co.uk.
What does vary by organization is the monitoring which will be implemented by the competent authority. Essential organizations get active monitoring, where important organizations reactive monitoring get.
Essential entities
- Organizations that are active within one of the very critical sectors with a minimum of 250 employees or an annual turnover of at least 50 million with a balance total of at least 43 million.
- Medium-sized providers of public electronic communication networks and services.
- Organizations that fall under the Critical Enterprise Resilience directive as a critical entity.
- Public authorities that: according to national law are recognized as such, are established to serve the public interest (without commercial purpose), are largely funded or controlled by the public, and are authorized to make binding decisions that affect citizens or businesses.
- Qualified providers of trust services and top-level domain name registries and DNS service providers, regardless of their size.
Important entities
- Organizations that operate in a highly critical sector and have at least 50 employees or a turnover of at least 10 million and a balance sheet total of at least 10 million.
- Medium-sized and large organizations that are active within one of the critical sectors.
Cybercriminals don't wait
Just because the Cyber Security Act is not yet in effect in the Netherlands does not mean you should wait to take action. Waiting longer will make your organization more vulnerable to attacks by cybercriminals. You can ensure that your company is NIS2 compliant before the Cybersecurity Act comes into effect. NIS2 is there to ensure cyber security, and by taking steps now, you are giving cybercriminals less opportunity to launch attacks on your business.
Want to learn more about what the NIS2 Directive and thus the Cybersecurity Act means for your company or schedule an NIS2 Board training in advance? Contact us and we will help you further.