ISO 27001
We guide you from your initial ISO 27001 risk assessment through your preparation for the external audit, which 100% successfully passes for our clients.
We guide you from your initial ISO 27001 risk assessment through your preparation for the external audit, which 100% successfully passes for our clients.

Achieve ISO 27001 compliance in the short term? Our experts are ready to ensure your security meets the requirements of partners, customers, and stakeholders – and they do so with a 100% Pass Rate. In other words, every organization we guide through ISO 27001 compliance manages to pass the external audit.
✓“We need to comply with ISO 27001 to win deals from competitors.â€
✓“Our customers expect proof that we handle their data with care.â€
✓“I don’t just want a quality mark—I want our security to genuinely improve.â€


Figure it out yourself, slow and uncertain
Guided, predictable and carefree
A structured, expert-led approach that takes the uncertainty out of the process.
Your ISO 27001 certificate is valid for three years, with surveillance audits in years 1 and 2 and recertification in year 3. We will also remain on board after that.
✓Understanding what certification requires from your organization
✓Overview of the steps toward the external audit
✓Free to download, no obligations
Feedback analytics developers with a team of over 250 people

Effectory processes sensitive employee data for over 1,200 organizations. The challenge was to continuously strengthen the information security system and have it grow with the high demands of customers, without disrupting daily services.

In close collaboration, we have refined the management system for both ISO 27001 and ISO 27701. With a dedicated point of contact, responsibilities have been clearly defined, processes secured, and the organization prepared for the external audit to achieve certification.

Within 6 months, Effectory achieved ISO 27001 certification without any bottlenecks. Security is now demonstrably in order for customers, security questionnaires are answered more quickly, and a solid, future-proof foundation is in place.

Nestor Security conducted the internal audits for both ISO 27001 and ISO 27701 for us. They really strike the right chord for us with a great combination of quality and feasibility. They are pragmatic, think along well with our needs, and the audits are well-organized.
 Wouter Buzing
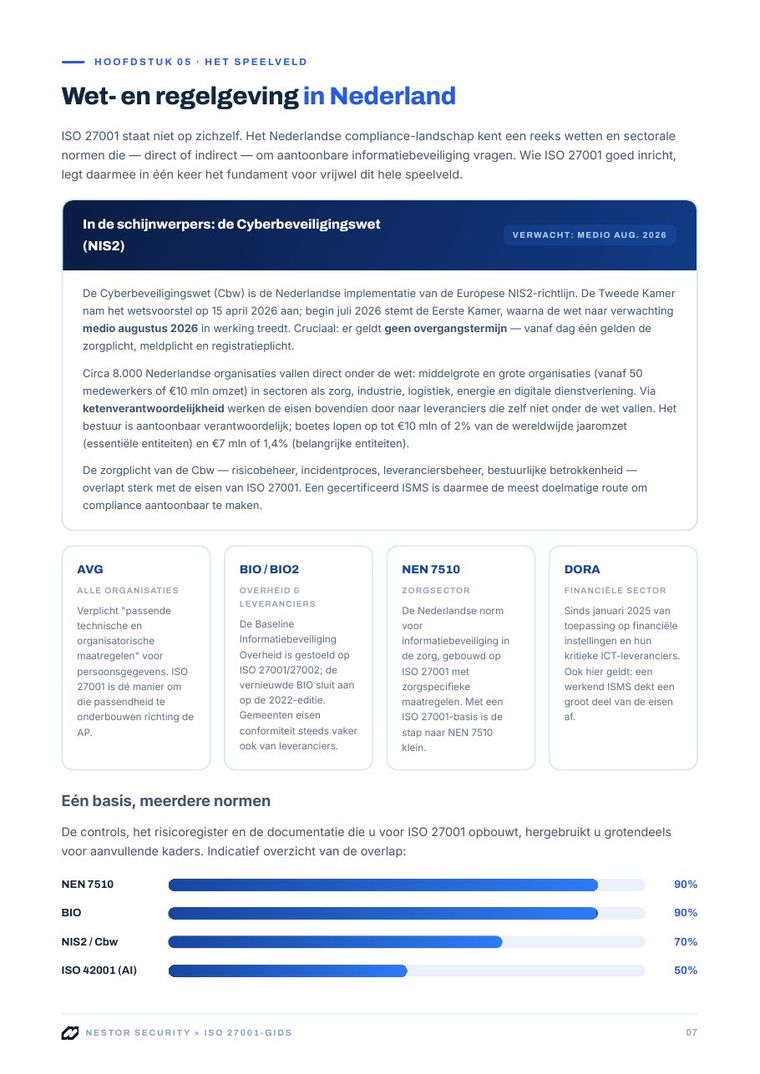
ISO 27001 certification provides a significant head start on implementing additional standards, thanks to shared controls and processes.
More than 90% overlap with NEN 7510
More than 90% overlap with BIO
More than 70% overlap with NIS2
A 50% overlap with ISO 42001
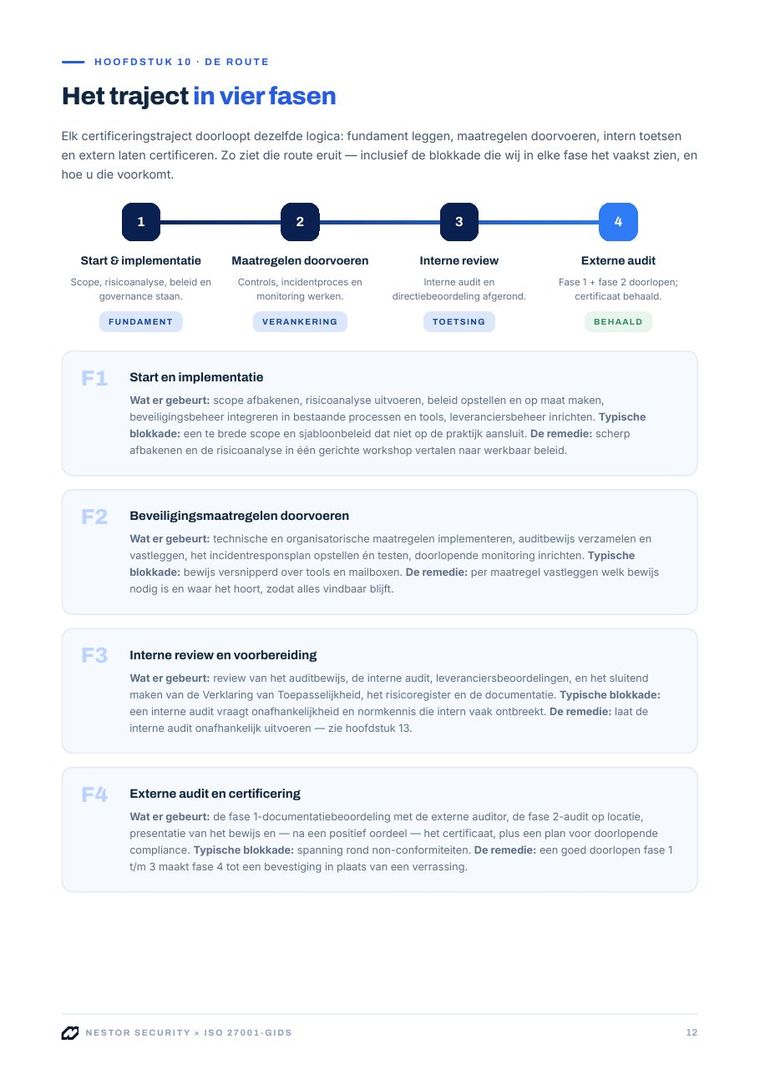
We guide you through the entire process, from the initial risk assessment to a successful audit. No generic approach, but advice that fits your organization.
We translate the requirements of ISO 27001 into concrete, workable measures. We set up policies, procedures, and risk management in such a way that your employees can actually work with them.
Together, we map out your information security risks and determine which ones require the most attention. This allows you to invest in a targeted manner and ensures you are never faced with surprises during the audit.
We prepare you thoroughly for the external audit and guide internal audits, management reviews, and annual surveillance. Certification is not an endpoint, but a foundation that we maintain together.
We don't just work for you, but also with you. By the end of the process, your employees will understand what information security means for them, and why it matters to your organization.
You are in good company with Nestor.
“Communication with Nestor Security was direct. The organization has a pragmatic approach and is a down-to-earth partner to do business with. As a result, the process went smoothly and quite quickly.â€

“We prefer to collaborate regionally as much as possible and like to hold meetings face-to-face. When you look at partners in the North, a few remain – and Nestor Security stood head and shoulders above the rest.â€

"Nestor Security has provided us with the internal audits of ISO 27001 and ISO 27701. They really hit the right chord for us with a good combination of quality and practicability. They think pragmatically, well with our needs and the audits were well taken care of."

You need to comply with ISO 27001 to land your first big deal, and fast. We connect you directly with experienced ISO 27001 experts, so you don't have to choose between speed and a thorough approach.
Ad-hoc security is no longer sufficient for your organization. It is time for compliance that scales with your employees, products, and markets, without disrupting your processes.
We integrate ISO 27001 into your organization's governance, risk, and compliance processes. We connect you with enterprise-grade tooling and a methodology built for scale.
ISO 27001, formerly known as ISO/IEC 27001:2013, is the international standard for information security. The standard provides organizations in any sector with a framework to establish and maintain an Information Security Management System (ISMS).
An ISMS is a collection of policies and procedures that limit the impact of a security incident. It is both the foundation and the result of implementing the ISO 27001 standard.
With an ISMS that complies with ISO 27001, you efficiently and cost-effectively monitor the security, quality, and availability of all data within your organization. In addition, it gives your customers, investors, and other stakeholders the confidence that you follow international best practices for information security.
An Information Security Management System (ISMS) is a framework of policies and procedures to mitigate the impact of a security incident. It forms both the basis and the result of implementing the ISO 27001 standard.
There are two types of ISO 27001 audits: internal and external. The internal audit is intended for your own compliance, but also to prepare you for the external audit so that you pass it on the first attempt. The external audit must be performed by a third party: a Certification Body (CB) with expert auditors. We provide you with all the checklists, documents, platforms, and expertise you need to efficiently conduct internal and external audits.
ISO 27001:2022 is the most recent version of ISO 27001: the international standard for information security management systems that you must comply with to become certified.
An ISO 27001 certificate offers organizations several benefits:
Building trust with stakeholders: An ISO 27001 certificate demonstrates your commitment to information security and strengthens your credibility with partners. That gives you a competitive edge and enhances your brand reputation.
Compliance support for laws and regulations: ISO 27001 certification helps you meet your business, legal, economic, and statutory obligations. By mapping your legal and regulatory requirements, you reduce the risk of costly data breaches—and the expensive legal proceedings and fines that can result from them.
Protecting personal data and intellectual property: The certification process provides you with an independent assessment of your information security approach. It also helps you safeguard your intellectual property and information resources while building evidence of implementation.
Preventing costly data leaks: a data breach is expensive. In 2022, the average cost of a data breach worldwide was approximately €4.3 million (IBM Security, 2022). With ISO 27001, you protect your information based on established processes and procedures.